

Companies on IMDA's SMS registry can still be spoofed
COMPANIES that have registered with the Infocomm Media Development Authority's (IMDA) Singapore SMS SenderID protection registry pilot can still have their sender IDs spoofed.
The registry pilot is meant to prevent scammers from being able to impersonate companies via SMS.
Some of the companies that have signed up for this pilot include DBS, Lazada and SingPost.
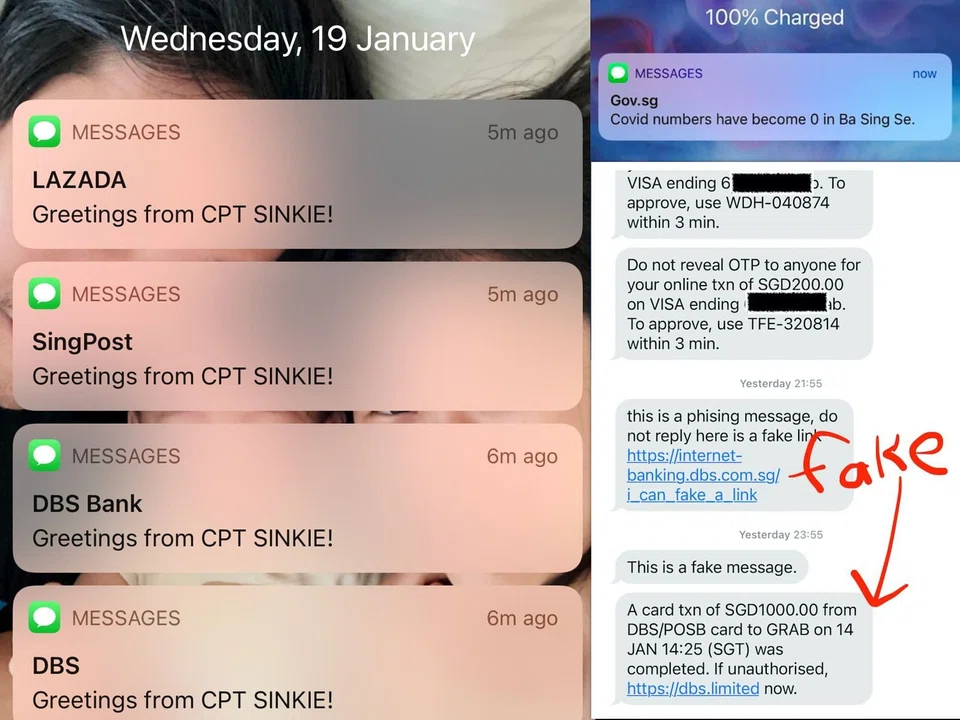
But an individual posting online under the name of Captain Sinkie said he has been able to send SMSes that appear to be from these entities as well as several others also in the pilot. He also found that at least 1 other scam has been reported on the r/Singapore subreddit.
Captain Sinkie, a founder of a programming school who asked to be known only by the name of Lee, had earlier started a petition to make the registry mandatory.
The petition has since garnered more than 2,000 signatures.
The Business Times (BT) has independently confirmed Lee's findings that spoofed SMSes can still be sent via online services.
On Monday, IMDA had urged companies to sign up to its pilot. This would include registering the SMS sender IDs they wish to protect as well as choosing the approved SMS aggregators that are allowed to send SMSes on their behalf.
The Mobile Ecosystem Forum (MEF), a global trade body, initiated the first pilot of such a registry in the United Kingdom. Ireland's registry was launched in July last year, while Singapore's registry was launched a month later.
In 2021, the MEF said more than 70 bank and government brands were registered. Over 24 banks and government agencies are directly participating and 352 trusted sender IDs have been registered.
It also noted that more than 1,500 unauthorised variants of sender IDs are being blocked on a blacklist that continues to grow.
BT has reached out to IMDA for comment.
TRENDING NOW

Genting Singapore trails MBS, but helps anchor Malaysian parent group’s finances

Siti Hasmah Mohamad Ali, wife of former Malaysian PM Mahathir Mohamad, dies aged 100

He built the Vingroup empire. Now South-east Asia’s richest man is handing some key roles to his sons

Why US midterm elections could power the next stock market rally

