



Asean’s patchwork of data regulations needs a revamp
Regional mechanisms and trade agreements often appear deceptively promising for data flows
SOUTH-EAST Asia’s data protection regulation landscape has witnessed significant activity in the past two years, including the enactment of new personal data protection laws in Vietnam and Indonesia, and the enforcement of the Asean Model Contractual Clauses (MCCs). For businesses, this means navigating an ever more complex and diverse regulatory terrain on personal data, constraining the region’s digital economy growth potential.
Existing regional efforts like the MCCs and trade agreements, however, are insufficient in harmonising national regulations, thereby failing to foster a business-friendly regional data landscape.
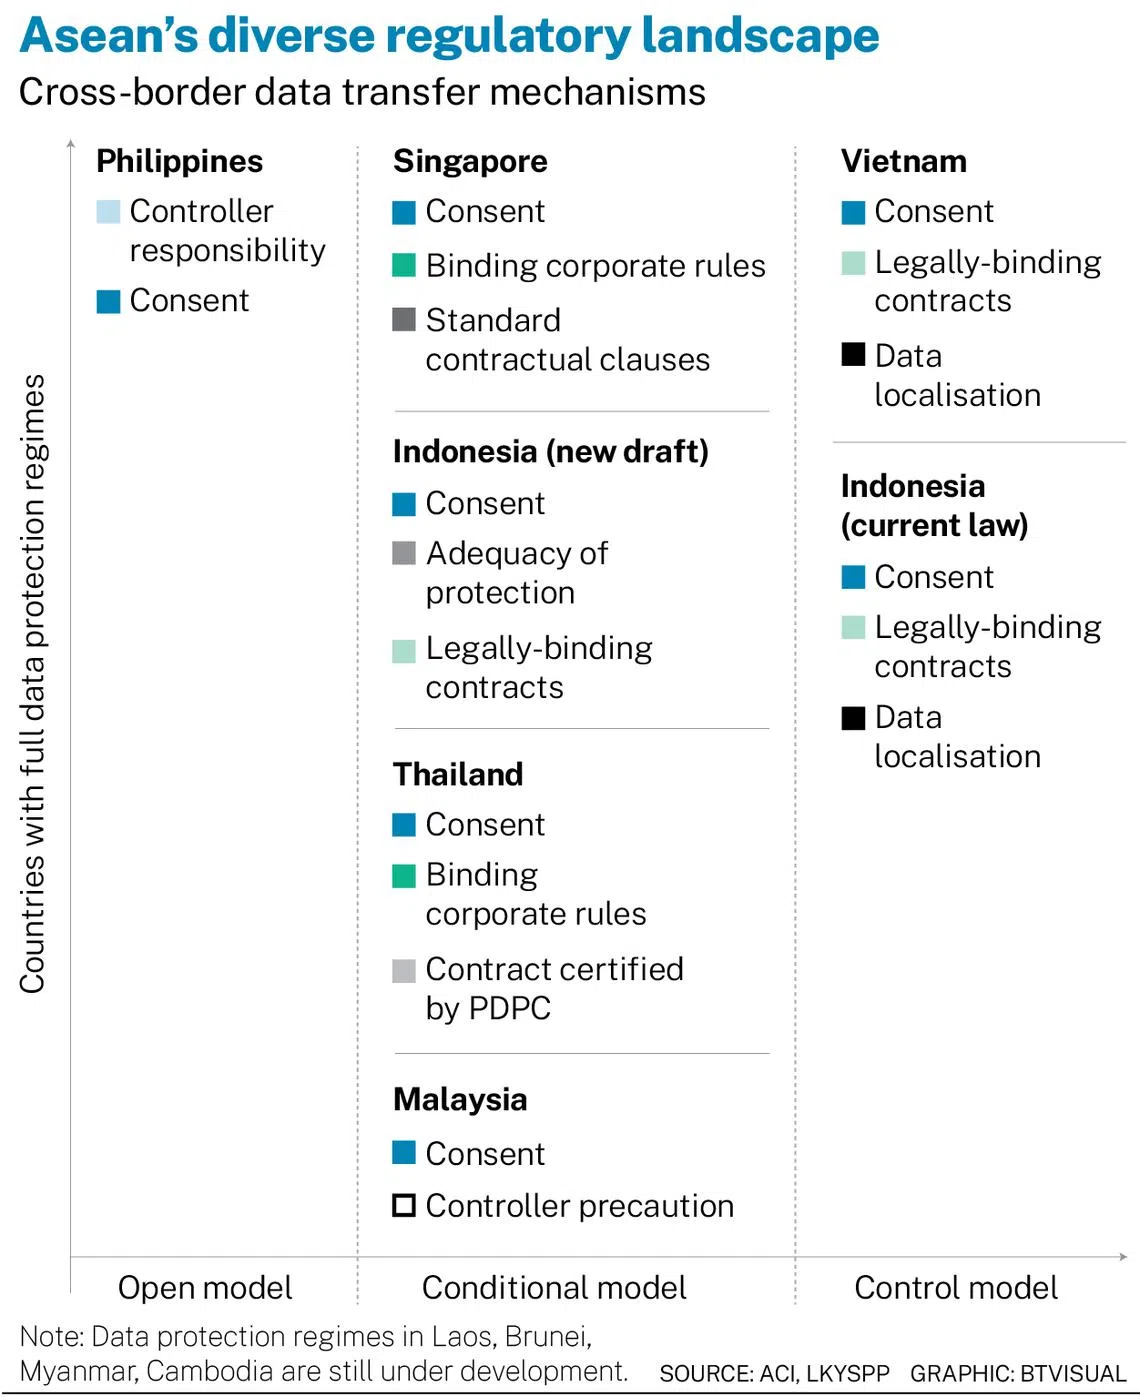
The significant disparities in personal data protection regulations across Asean countries create formidable barriers for businesses. Besides legal frameworks being at various stages of development, the content of data protection laws also differs significantly due to widely different national interests. At the most liberal end, the Philippines takes a very business-oriented approach with minimal cross-border data transfer restrictions, while Vietnam, on the other end of the spectrum, heavily emphasises national security and requires extensive data localisation.
Even among countries with similar cross-border data transfer requirements, such as legally binding contracts, the exact provisions differ, making compliance challenging. Firms operating in multiple markets must sign and adhere to multiple contracts. This not only requires a high degree of legal knowledge, but also hampers business fluidity.
Ineffective regional efforts
To overcome these challenges, regional initiatives aim at smoothing companies’ international data transfers. At the Asean level, the MCCs can be incorporated into legally binding contracts between the data-transferring parties. At the international level, the Asia-Pacific Economic Cooperation’s Cross-Border Privacy Rules (Apec CBPR) is a certification scheme for data handlers that allows for unrestricted data transfers between two certified parties. However, it is only applicable in Singapore, the Philippines, and seven non-Asean countries.
Both MCCs and Apec CBPR have not succeeded in bridging the gaps and creating a business-friendly data environment in South-east Asia, and key challenges remain for firms.
While the Asean MCCs ease companies’ compliance burden, their effectiveness is limited by countries requiring tweaks in the stipulated clauses. This again increases the legal burden as multiple modifications must be added for different transfers. Additionally, only Singapore has legally endorsed MCCs in its data protection regulation, which increases uncertainties for companies transferring data across Asean using this method.
Even if MCCs or CBPR mechanisms are correctly employed, interoperability issues still hinder smooth transfers. Provisions on the reasons for which data can be collected and processed or how sensitive data must be treated differ, meaning that firms must adapt their data operations depending on the country where data was collected.
Small and medium-sized enterprises (SMEs) face comparatively larger compliance costs. As Desmond Chow, director of P2D Solutions, a consultancy working with SMEs on data protection compliance, points out: “For SMEs, the compliance is a lot tougher because they currently really do not have enough resources – not just for handling overseas transfer compliance, but from a general (Personal Data Protection Act) compliance standpoint.”
Data localisation
While most Asean countries are leaning towards liberalising data flows, Vietnam is an outlier. Its new data protection regulation requires informing the Ministry of Public Security about data transfers, impact assessments, and potential data localisation, adding complicating layers to businesses operating in Asean. According to Jeth Lee, Microsoft’s Asean head of legal and regulatory affairs, “most companies may wait to transfer data overseas until they get an indication of no-objection from the Ministry of Public Security”, even if this involves negative business consequences.
If data cannot be processed abroad, it also means that Vietnamese citizens and businesses may have challenges accessing services that require employees or servers abroad, save where specific conditions are adhered to.
The fix
To address these multifaceted issues, it is necessary to go beyond Asean MCCs and align provisions in national-level regulations, expand the number of countries participating in international mechanisms, and support firms, especially SMEs, in becoming compliant.
Some have placed their hope in external influence from countries like the United States and China, or groups such as the European Union (EU), to push forward harmonising data protection frameworks in Asean. However, an examination of trade agreements suggests that this is not happening yet. We found that trade agreements Asean countries are party to are often riddled with exceptions when it comes to provisions on free data flows.
The Comprehensive and Progressive Agreement for Trans-Pacific Partnership (CPTPP) and the Regional Comprehensive Economic Partnership (RCEP) – two major trade pacts in the region – both exclude overriding national interests from free data flow clauses. While what constitutes a legitimate national interest can be disputed under the CPTPP, it is completely at the discretion of the domestic government under the RCEP. Additionally, under both agreements, almost half of Asean signatory countries have exceptions to the implementation of these clauses of two, five, or even eight years.
Beyond the superpowers, Singapore and Australia emerge as the key internal and external influencers on cross-border data flow policies in Asean, as they have the highest number of trade agreements signed with Asean member states that contain provisions on free data flows. Meanwhile, we found that most trade agreements signed by Asean countries remain either bilateral, or signed by just a few countries. Such bilateral agreements between key regional and external partners may be an interim solution until large-scale harmonisation can be achieved.
In the near-term, reducing ambiguity and raising awareness of personal data regulation compliance should be prioritised to mitigate the negative impact on business activities, as this is easier to achieve than harmonising data regulatory frameworks across the region. Rules and guidelines should be formalised, and SME-specific support provided through awareness-raising and training workshops, as well as increasing government-industry collaboration.
In the longer term, coherent cross-border data transfer mechanisms across the region and perhaps at an even larger scale should be the goal, which can be supported by interim solutions of harmonising existing national regulations and signing bilateral agreements. The release of the joint guide to Asean MCCs and EU Standard Contractual Clauses between Asean and the European Commission in June is a promising step in driving coherence.
The writers are from the Asia Competitiveness Institute, Lee Kuan Yew School of Public Policy, National University of Singapore. Liu Jingting is a research fellow. Ulrike Sengstschmid and Ge Yixuan are research analysts.






