

The challenge of keeping offshore drilling secure
By connecting their entire fleet of rigs to a single platform, contractors can cut through complex systems and detect potential threats more promptly.
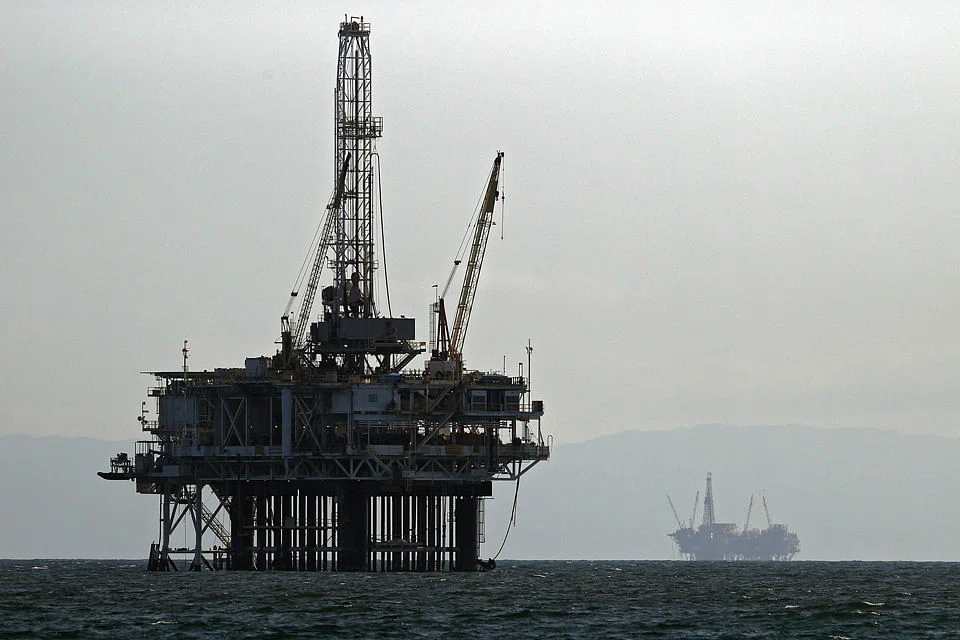
THE oil and gas industry presents a unique and complex cybersecurity profile. A serious attack disabling offshore drilling rigs carries devastating consequences not just for the organisations that own the infrastructure, but for wider global economies as supply is disrupted. Due to the often precarious and isolated nature of offshore facilities, such attacks could easily go beyond the digital to directly endanger real human lives.
At the same time, organisations face pressure to keep up with the wider business world by digitising and automating their operational technology (OT) systems. For example, Malaysia-owned Petronas uses a real-time data management solution to manage and analyse its rig-site drilling operations remotely. While digitalisation brings unprecedented benefits, the Industrial Control Systems (ICS) and Supervisory Control and Data Acquisition (SCADA) systems at the heart of the industry are notoriously challenging to secure in the digital age.
In August 2012, hackers launched an attack on Saudi Aramco, which partially or completely wiped out 35,000 computers. This put the company's business into turmoil as all of its global offices had to go offline for five months to contain the spread of the Shamoon virus. More recently in 2019, Hibiscus Petroleum, a Malaysian firm, faced a cyberattack which prompted a partial system shutdown, although operations were fortunately unaffected.
There is also the risk of a large-scale cyberattack on offshore infrastructure as part of offensive nation-state activity in Asia, where oil rigs in the South China Sea are potential targets of furore from countries involved in territorial disputes. Their systems also remain vulnerable as a point of entry for criminals seeking entry into company networks and valuable data such as financial information and intellectual property.
One of the biggest issues around offshore technology is its fragmented nature. Assets and infrastructure often use multiple different systems provided by different external contractors. Looking at floater assets for example, standard drilling ships and semi-submersibles typically include four major independent OT networks. Each of these different elements will generally be following its own communication protocols and using different automation equipment, making it extremely difficult to gain a single unified view of the network as a whole.
POTENTIAL VULNERABILITIES
This fragmented approach introduces multiple different potential vulnerabilities that can be exploited by threat actors. For example, the contractors responsible for maintaining the systems will typically be using remote access to carry out their duties. Attackers can compromise these privileged third parties to gain access to the systems.
Compounding this, a drilling ship's OT network is rarely air-gapped and is instead connected directly to the rig contractor's main IT network, which is in turn connected to the Internet. This means that, in addition to the risk of the ship itself being disabled, offshore assets can easily be used as a stepping stone to execute attacks on the main IT network of the parent organisation.
The multifaceted nature of OT security is recognised by governments such as Singapore's, whose Cyber Security Agency identified oil and gas as a key sector in its OT Cybersecurity Masterplan, unveiled in 2019.
Despite the significant threat posed by these common operational practices, however, it is apparent that the risk cannot be easily managed by the rig contractors. Each network is managed in a complete silo by its respective contractor, which means there is no cohesive visibility of the assets across the OT environment.
Further, traditional IT security monitoring products are not equipped to deal with the proprietary nature of the OT protocols being used by different assets throughout the floater's network. This disjointed approach is an additional boon to cyber attackers, making it much more likely that any suspicious network activity will go undetected.
However, while this fragmented environment presents significant security challenges, it is possible for rig contractors to regain control and oversight with the right approach and tools.
Attaining visibility of all of the disparate OT systems is essential to securing offshore infrastructure against malicious cyber activity. This is most effectively achieved with the use of a single, vendor agnostic security platform that is able to integrate with the different systems being used by each rig contractor involved. As mentioned, traditional IT management tools usually struggle with OT systems because of the number of different proprietary technologies, each with its own particular protocols. Therefore, successfully integrating with multiple OT systems demands a specialised solution that has been designed with the oil and gas industry in mind.
The main objective is to be able to monitor all traffic across the network, but how this is achieved will depend on the specific configuration being used. A network that features a main switch that aggregates all the traffic can be monitored from this single point.
Meanwhile, a network that is more segmented, or features independent level-one clusters can be monitored by port-mirroring each of the relevant switches and sending copies of the data packets to another main switch. Here, a balance needs to be struck between achieving maximum coverage with a minimal footprint on the network.
PRIORITY
Because the impact of a successful attack on the infrastructure itself has such devastating consequences, the priority should be replicating and monitoring all traffic that directly impacts physical processes.
Following this, the next objective is to identify and monitor strategic switches such as intersection points between network segments and working zones. This includes the intersection between IT and OT networks, which present opportunities for lateral movement by threat actors.
Once the key switches are identified and connected, the most effective approach is to use threat monitoring powered by machine learning to fully automate the process. The machine learning tool can be trained to recognise normal network behaviour for the rig, enabling it to instantly detect and flag any anomalies.
By connecting their entire fleet of rigs to a single platform, contractors will be able to cut through the opaque complexity of the typical rig OT arrangement and finally gain visibility of any potential threats, regardless of where they emerge.
TRENDING NOW

DBS, OCBC, UOB rout lops billions off STI as inflation, rate concerns spook investors

Grab CEO’s wife Chloe Tong on life with Anthony Tan and finding her purpose

OCBC sheds S$8 billion in value as shares close nearly 6% down; analysts cautious on banks

Deal between tycoon friends sparks scrutiny of Philippine power sector

