

Will cybersecurity blunders hurt chances of digibank hopefuls?
Digibanks offer more complex digital products so the 'attack surface' is far wider, says a CTO; every innovation or additional service within a digital bank increases this attack surface
Singapore
THE data privacy lapses at Razer and Grab that recently came to light raise questions about how ready digital bank hopefuls are in tackling banking's stringent security demands.
With consumers' most sensitive data at stake, banks are governed by security regulations far stricter and more specific than what other companies are used to. Digital bank hopefuls failing to understand and adjust to these new standards could put a dent in their own ambitions, observers said.
Last Thursday, Singapore's privacy watchdog disclosed that Grab was fined S$10,000 in July 2020 after a 2019 update to its mobile app compromised the safety of data belonging to more than 21,500 drivers and passengers. Grab was chided for making a similar mistake twice and breaching data protection laws for the fourth time in two years.
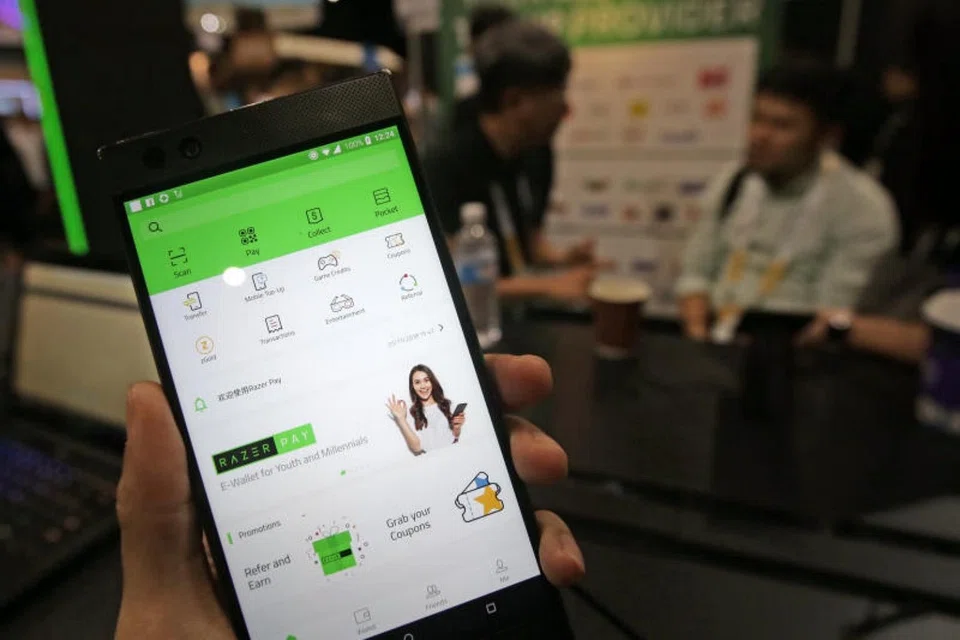
Another digital bank applicant, Razer, was discovered by a cybersecurity consultant to have exposed the personal data of about 100,000 customers in August this year. Of particular concern was how the company only began notifying affected customers on Wednesday, after the incident was reported by the media.
While both companies have fixed the issues, reviewed their systems and reaffirmed their commitment to data protection, their blunders highlight how seriously companies need to take cybersecurity if they hope to step foot into the complex world of banking.
The Monetary Authority of Singapore (MAS) has a firm stance on this. It has been strengthening its regulatory regime with its Cyber Hygiene Notice that came into force in August 2020, making the key requirements of the existing Technology Risk Management (TRM) guidelines legally binding for MAS licence holders.
As it is, non-financial companies mostly come under the purview of the Personal Data Protection Act (PDPA). But the PDPA does not specify in a fine-grained way what companies must do to protect data - just that they need to protect it, and if they do not, there are penalties, said Kevin Lee, chairman of cybersecurity firm Horangi.
"The MAS TRM guidelines specify in more detail what cybersecurity practices you need to have. And you need to be compliant to it as an MAS licence holder. So even if you never suffer a breach, you can be found to be non-compliant," said Mr Lee, a former data science executive at GIC, Grab and Palantir.
MAS managing director Ravi Menon highlighted in May 2019 that, given their role as repositories of public monies and conduits for payments, banks in particular must meet higher cybersecurity standards.
The consequences of a data breach at a bank could potentially be disastrous, experts told The Business Times. "The data that a bank holds on its customers includes the information about their location, preferences, financial well-being, the places that they visit and their social circle," said Dmitry Volkov, chief technology officer at Singapore-based cybersecurity firm Group-IB, which has worked with top international banks.
The wealth of information gives financially-motivated cyber criminals greater targeting opportunities, while ordinary fraudsters will have more chances to lure people into their scams.
Mr Volkov noted that digital banks are different from traditional banks in that they do not have their own network of ATMs and offline branches, and they tend to have less systems to maintain. "But at the same time, digibanks offer more complex digital products so the "attack surface" is far wider. Every innovation or additional service within a digital bank increases this attack surface. Therefore, it's extremely important to constantly research and hunt for threats relevant for the digital banking industries all over the world," he said.
A lapse in data security could have deep implications on which digital bank a consumer chooses to transact with. "Obviously convenience and the user experience are important factors too. However, increasingly we are seeing a consumer-driven need to feel that one can transact safely online," said Charmian Aw, a lawyer at Reed Smith who specialises in matters of data and technology.
Tech companies that have long gotten used to innovating quickly might now have to grapple with the cybersecurity conundrum of "if you make it too secure, you make it less agile" (though the two are not always on opposite ends of the spectrum).
David Siah, vice-president (SEA-Australia) at the Center for Strategic Cyberspace and International Studies, believes digital banks would have to err on the side of caution.
Traditional banks have had a lot more time to learn where the gaps are in securing their infrastructure and processes, Mr Siah said.
The new breed of digital banks, on the other hand, would have to learn the ropes in matters such as governance and threat detection.
Then there is the matter of resources. A 2019 report from Forrester noted that global banks like JPMorgan Chase and Morgan Stanley spend up to US$600 million on cybersecurity each year.
Worth noting, however, is the fact that cybersecurity and data protection is not an issue that is fixed just by throwing money at it, said Varun Mittal, global emerging markets fintech leader at EY. It could boil down to something as simple as how access to systems is controlled, or how quickly a mistake is caught.
German neobank N26, an upstart darling, made headlines early last year after customers complained about its long response time even after reports of potential fraud. To no one's surprise, it became the subject of public backlash.
With so many potential pitfalls and a high degree of accountability, digital bank aspirants must hence fully understand the demands of building a secure platform and demonstrate that their capabilities are up to the task.






