

Driven to win
CrowdStrike CEO George Kurtz - who also happens to be a top driver in car-racing circuits - has placed his company in top gear so as to beat cybercriminals before they can hit.
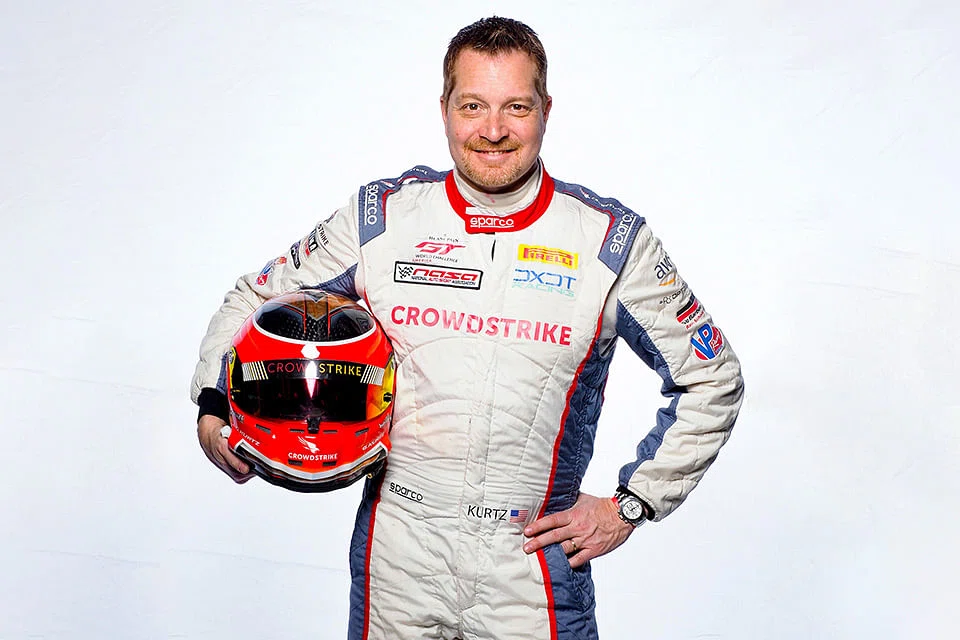
GEORGE Kurtz has two big passions.
One is catching cybercriminals and the other is competitive car racing. What's highly notable is that he's equally fervent about both and right near the top in terms of achievements in these very demanding fields.
As the co-founder, president and CEO of one of the fastest-growing cybersecurity companies in the world, CrowdStrike, he is pioneering a new way of providing cybersecurity to companies. And, as a race driver in the GT World Challenge America circuit, he has won a number of races since starting to drive competitively around 10 years ago.
As has become the norm in these pandemic times we meet and talk over video, with Mr Kurtz speaking from Phoenix, Arizona in the United States. To a question on how he manages his two very different passions, he responds that there are a lot of similarities between the two and that helps.
"When you look at racing and you look at cybersecurity there are a lot of analogues. A team of people working together make CrowdStrike successful. Similarly, in competitive racing, it is the team and not just the driver who make a top-podium finish possible."
He explains that in competitive racing, everything has to work perfectly and for that "you need to look at the minute details". "I won a race recently by two-tenths of a second and that was made possible because the whole team looked at the minute details of both the car and the race strategy. Similarly, when we build something at CrowdStrike we put a lot of attention to the minute details so that the products are the best in class," Mr Kurtz says.
Rapid expansion
CrowdStrike was set up in 2011 as a SaaS (software as a service) solutions provider that protects endpoint devices within an organisation's computer network through the cloud. Its products use artificial intelligence (AI), machine learning (ML) and other advanced technologies to provide cybersecurity protection.
The company did a highly successful IPO (initial public offering) last year in June where it raised more than US$600 million, valuing the firm at nearly US$7 billion at that time.
With work-from-home guidelines in force around the world, the demand for CrowdStrike's cloud-based endpoint security has gone up dramatically and the Silicon Valley company has been adding new customers. Market analysts note that the company's topline and customer base are expanding rapidly and it is on track to reach US$1 billion in annual revenues within the next couple of years.
Asked what made him set up the company in 2011, when the concept of providing cybersecurity to endpoint devices through the cloud was not very popular, Mr Kurtz reveals that the idea came to him when he was working at cybersecurity vendor MacAfee.
"It's an interesting story. I set up a company called Foundstone in 1999 which I sold to MacAfee in 2004. After that, I spent the next seven years running different business units in MacAfee. I eventually became the company's CTO (chief technology officer) with oversight over the entire product portfolio.
"This provided me with two major takeaways. One was that companies were spending a lot of money on cybersecurity and yet they were not getting the outcome that I thought they deserved. That was because the whole industry was focussed on the detection of the malware and not on preventing the network breach. I looked at it in a different way and asked: 'Why don't you focus on the outcome (that is, network breach and its associated implications) rather than on the infection mechanism?'," Mr Kurtz recalls.
The other major point, he says, is that the industry at that point, circa 2011, did not have a company which provided security-as-a-service, similar to how companies like Salesforce provided software-as-a-service. "So, my idea was to become the Salesforce of security and build a platform from ground up that is cloud-native and deliver the outcomes the customers deserve.
"I can tell you in 2011 the idea of delivering cybersecurity to endpoint devices from the cloud was not popular. People said: 'You are crazy, it is never going to work; we are never going to use the cloud'.
"Obviously when we look (at it) today, we can say we were well ahead of the curve and correctly foresaw that the cloud will play a much-bigger part in cybersecurity."
In 2010, Intel bought over MacAfee and that provided Mr Kurtz an opportunity to leave and strike out on his own.
Among his first backers was the private investment group Warburg Pincus. "I had a connection with the Warburg Pincus guys. For years they wanted to make an investment in Foundstone even when I was selling to MacAfee. They would call me every year and ask me if I wanted to sell.
"So, I thought I would talk to them about the new venture," says Mr Kurtz, adding: "I put together 25 slides for the presentation and I got US$25 million from them. That was really the start of CrowdStrike. It is kind of ridiculous that I could get that kind of money as VC (venture capital) funding after showing a PowerPoint presentation."
Following Warburg's lead, many other major VC financiers like Accel, Google, General Atlantic and IVP invested in CrowdStrike. "We took half a billion dollars of VC funding before we went IPO," Mr Kurtz notes with a hint of pride.
How it works
Explaining how his products work, Mr Kurtz notes that endpoint security in 2020 is about protecting workloads in the cloud and not necessarily just computers and servers. "So, anything with computer network and storage within an organisation is protected by us. We have an agent piece of software that runs on any one of these 'endpoints' and essentially does a few things.
"One, it collects diagnostic information about what is happening in the network system, that is, what processes are running and what's happening in the background. This information is organised in a graphical format, which is really important. This allows us to look at all the events and link them to each other. This is important because if you look at individual events, they may not seem problematic but when you string them all together then they could start to look problematic," he observes.
CrowdStrike applies AI-driven analytics to these events and "essentially we are looking for bad things happening on the system". It could be a piece of malware but it could also be malicious activity that does not use malware, Mr Kurtz says, and adds: "We are able to identify and prevent that."
He points out that CrowdStrike differs from traditional anti-virus software vendors in that it looks at what the system (the organisation's computer network) is doing instead of what the users are doing.
"We use this information in various modules to identify vulnerabilities and do forensic analysis and investigate what is happening in the system.
"And once we have collected the data, we don't have to collect it again. The beauty of our business model is that we collect the data one time and then we have all these modules that use the data and we sell them with different workflows and this generates a high margin opportunity for us."
The CrowdStrike CEO uses a bank robbery analogy to explain further. "Suppose someone were to walk into a bank and go to the teller, ask for cash, get it and then walk out of the bank. Is that a robbery? No.
"But suppose a guy comes to the bank, has a mask and a gun. He walks up to the teller, who gives him the cash. Now you have a chain of events in which the teller giving the cash is not a malicious activity. Rather, just showing up to the bank with a mask and a gun is a malicious activity. So, when you put them all together and link them, then it is an activity; it's a stream of activities that is malicious. That is a big difference between what we do and what the traditional anti-virus vendors do," Mr Kurtz says, adding that CrowdStrike looks at the pattern of activities to identify threats.
Asked about the highly sophisticated cyber threats presented by well-funded criminal gangs as well as nation state-backed hackers, Mr Kurtz notes that his company has agents in 176 countries and "we collect information on around three trillion online events every week".
"In other words, we collect more events in a day than the number of tweets that Twitter has in a year. This data is used for our AI training. The interesting part is that while the bad guys know all about their attacks and what methodologies they use, they don't have the information about every attack that happens. We, on the other hand, crowdsource that information and use it to build defences. We call that community immunity," says Mr Kurtz.
Explaining this from the perspective of a user, he explains: "As a user, I click on a file and some program starts running in the background. I don't know if that is malicious or not. But behind the scene, if it starts to run extra processes, starts to delete back-up files or starts to encrypt files, then that's a piece of ransomware. You have to look at all the events together and that's what we call 'Indicators of Attack' and what our threat graph does is that it essentially assembles all that in real time."
To a question on how cyber threats have evolved, Mr Kurtz notes that years ago, in the early days of cybersecurity, hackers would break into a network or a computer and look around without doing much damage.
"Then the focus shifted to data exfiltration and after that to data destruction - attempts to wreak something or encrypt something and try to extort money (ransomware) from a crime perspective."
According to Mr Kurtz, what has become really scary is the data-destruction part. "We have seen that happen with the NotPetya cyber attack (in 2017) and in the similar ransomware attacks. It's bad enough to have your data stolen but when you can't ship a product because your network is down, that is problematic. Some of the companies that got hit with NotPetya spent hundreds of million dollars to recover and they almost went out of business. They were some really big companies," he says.
Security has moved from something that is nice to have to a "must have" and is now a part of business resiliency, points out Mr Kurtz, adding: "If you are not doing the right things you could actually create a risk that would take down your company."
Today it's a much different world from one where a kid sitting in the basement hacks your computer for fun, the CrowdStrike CEO notes.
Massive business
There are three broad groups of threat actors today, he says. These are the nation states, crime syndicates and hacktivists who hack for causes. "Hacktivism is on the rise in today's environment. But the nation state has the best techniques and tools. What we are seeing is the blending of nation states with e-crime. And e-crime has exploded. It is a massive business."
On state-sponsored hacking and e-crime, Mr Kurtz uses an example: "I have this iPhone. It has a GPS (global positioning system). GPS started out as a military technology and today we have it on phones.
"Similarly, what we are seeing is a trickle-down from the toolbox of nation states whereby some of the most sophisticated hacking tools are unfortunately finding their way to criminal gangs. While the e-crime groups can't figure out how to make the nuclear bomb they can sure detonate it. When they get these advanced attack vectors, they can weaponise them and make a massive amount of a money."
After its successful IPO last year, CrowdStrike has been racing ahead, so to speak, in terms of financials, having delivered a stellar first quarter buoyed by increased demand for its cybersecurity solutions. However, that is unlikely to satisfy its CEO.
Mr Kurtz comes across as a man who has many more mountains to climb and conquer. Asked what drives him, he returns to a racing analogy. "One of the biggest aspects of motor racing is that even if you win you say: 'What could we have done better?'.
"That is the mindset we bring to CrowdStrike. Every day we look at how we can make our products better. What can we do better for our customers? When I interview people, I ask: 'What drives you more, your will to win or your hatred of losing?'
"Some people say: 'I love to win'. That's great but the best people in the world hate to lose more than they love to win," says Mr Kurtz.
He adds that after you win a race, you forget about it soon after, but if you lose it stays with you for weeks. "The best guys - Michael Schumacher, Lewis Hamilton and all other racing champions - hate to lose more than they like to win."
So, in sum, the engine that drives George Kurtz, race driver and CEO of CrowdStrike, is his loathing for losing any battle. Cybercriminals will certainly take note of that.
And yes, if anyone is wondering, the fancy set of wheels in his garage is a street-legal Mercedes AMG GTR which he admits he drives fast. And he thinks car prices are ridiculously high in Singapore.
GEORGE KURTZ
President, CEO and co-founder CrowdStrike
1970: Born in New Jersey, USA
EDUCATION
1988-1992: Bachelor of Science in Accounting, Seton Hall University, South Orange, New Jersey
CAREER
1991-1998: Manager, Security Group, PricewaterhouseCoopers
1998-1999: Senior manager, Security Profiling Services Group, Ernst & Young
1999: Co-published Hacking Exposed
1999-2004: Founder and CEO, Foundstone
2004-2006: Senior vice president and general manager, Risk Management, McAfee
2006-2008: Senior vice president, Enterprise, McAfee
2008-2009: Senior vice president and general manager, Risk and Compliance Business Unit, McAfee
2009-2011: Executive vice president and worldwide chief technology officer, McAfee
2011-2012: Executive in residence, Warburg Pincus
Since 2012: President, CEO and co-founder, CrowdStrike
Decoding Asia newsletter: your guide to navigating Asia in a new global order. Sign up here to get Decoding Asia newsletter. Delivered to your inbox. Free.
Share with us your feedback on BT's products and services
TRENDING NOW

Grab CEO’s wife Chloe Tong on life with Anthony Tan and finding her purpose
Jacqueline Loh to step down as MAS deputy MD in senior leadership reshuffle
Why 1 in 2 young Singaporeans who said ‘no kids’ now say ‘yes please’: new study
Private home prices accelerate with 1.4% rise while HDB resale values dip further in Q3: flash data

