

Beef up cyberdefences now, CSA urges all organisations, as reported incidents triple
The advisory comes after a string of data breaches across various sectors in recent weeks
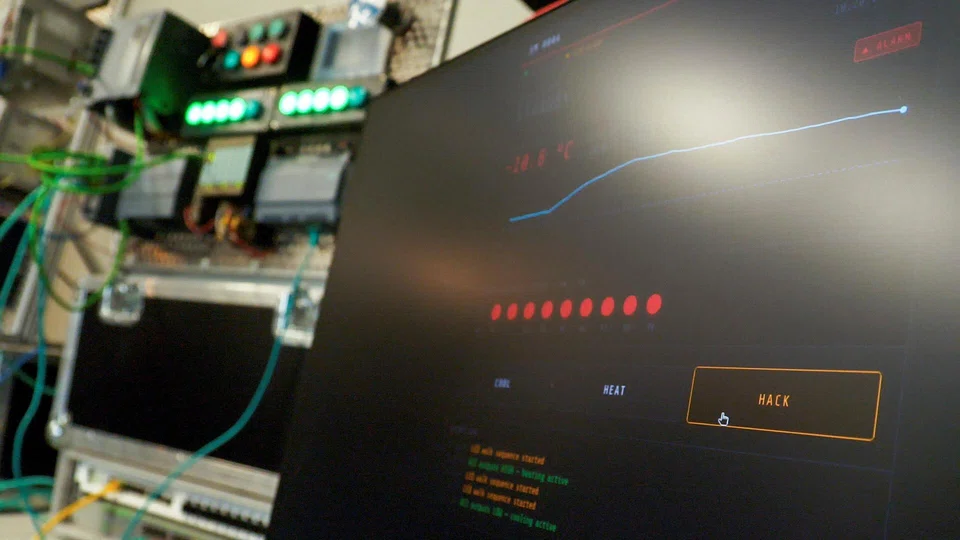
[SINGAPORE] All organisations in Singapore, regardless of size or sector, should take steps now to strengthen their cyberdefences amid a recent trebling in reported cyberincidents here, said the Cyber Security Agency of Singapore (CSA) on Friday (Nov 13).
The advisory comes after a string of cyberincidents across various sectors in the past weeks, affecting Singapore organisations or their service providers, and a rise in significant data breaches reported to the Personal Data Protection Commission (PDPC) over the past week involving well-known organisations.
CSA advised organisations to take action as cyberthreat actors are increasingly exploiting exposed vulnerabilities and poorly secured systems, with artificial intelligence allowing hackers to speed up attacks.
The agency said that since September, the average monthly number of reported cyberincidents has been three times the average for the January-to-August period.
“These incidents do not appear to be part of coordinated campaigns targeting Singapore but reflect a broader global trend of opportunistic attacks,” CSA said. “Some incidents have also involved compromised third-party suppliers, underscoring the importance of managing supply-chain risks.”
In a separate Friday statement, PDPC said that the data breaches it observed arose from attacks exploiting a range of common vulnerabilities in information technology systems.

Similarly, there was no clear connection between the incidents, with some related to global data breaches.
PDPC commissioner Denise Wong said that organisations should give the recent increase in reported data breaches “urgent attention to avoid becoming victims”.
CSA CEO Gwenda Fong said that for business leaders, even those that do not have dedicated IT or security teams, “cybersecurity should be on your agenda”.
CSA noted that hackers are actively scanning the Internet for vulnerable systems, and organisations can become victims even if they are not specifically targeted. “The growing use of artificial intelligence by threat actors could further accelerate the discovery and exploitation of vulnerabilities, reducing the time organisations have to secure their systems.”
The agency urged organisations to prioritise the following when taking immediate steps to protect themselves:
- Secure Internet-facing systems;
- Promptly patch known vulnerabilities;
- Put in place multi-factor authentication; and
- Monitor for suspicious activities.
“Organisations should also ensure that their business continuity plans are ready to be activated in the event of a cyberincident,” it added.
At least 12 cyberincidents involving Singapore organisations or their service providers were reported between Oct 24 and Friday. Most involved confirmed or possible exposure of personal data, ranging from names and contact details to identity card numbers and travel itineraries.
Six of the 12 incidents involved healthcare and community care organisations.
The Ministry of Health said on Thursday that the six healthcare-related incidents had caused no disruption to patient care. It was unaware of any unauthorised access to patient health records and was following up with the organisations involved.
It also asked public healthcare institutions and health technology agency Synapxe to step up monitoring of cyberthreats, and urged private providers to strengthen their safeguards.
The first incident was reported on Oct 24, when healthcare services provider Alliance Medinet said the personal data of about 110,000 members had been compromised. Insurers such as HSBC Life, Income Insurance and Singlife, which are customers of Alliance Medinet, were among those affected.
On Nov 3, personal finance portal MoneySmart said an unauthorised party had copied personal data belonging to some customers in Singapore and Hong Kong. The information potentially exposed included identity card numbers and financial details.
That same day, Singapore Airlines said data from about 46,000 booking records had been accessed in a breach at its booking technology provider Amadeus. The data included names, booking references and travel itineraries. Travel document details may also have been accessed for about 620 records.
On Nov 6, telco M1 said a breach had compromised customer data including names, identity card numbers, dates of birth and home addresses. On the same day, telemedicine provider Doctor Anywhere separately reported that users’ personal data had been leaked. Clinical records were unaffected.
Four days later, SPH Media said cyberattacks had affected 9 per cent of its database, exposing some customers’ personal data. The company said payment card details and financial information were unaffected.
Also on Tuesday, Sats said a breach of its Tappee meal-ordering app had compromised student data at four schools, including names, concession card numbers and financial assistance status. A small number of records contained information such as students’ weight and allergies. THE STRAITS TIMES
Decoding Asia newsletter: your guide to navigating Asia in a new global order. Sign up here to get Decoding Asia newsletter. Delivered to your inbox. Free.
Share with us your feedback on BT's products and services






